Hackers Hit European Supermarket Freezers. Could the US Be Next?
 Chris Summers Owen EvansUpdated 6 days Ago8 Mins read
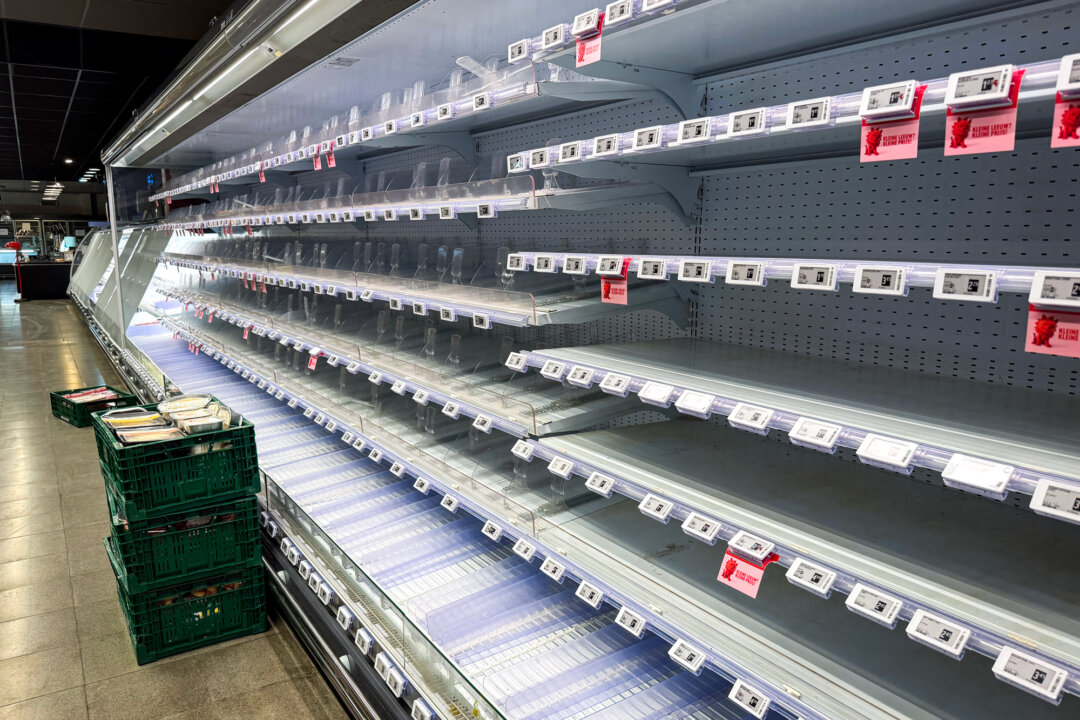
Cyberattackers have remotely adjusted supermarket refrigerators’ temperatures, causing them to overheat, in at least eight European countries this month, following a series of attacks in France in October.
The cyberattacks in Belgium, Estonia, Germany, Ireland, Italy, the Netherlands, Portugal, and Sweden led to food being spoiled. The incidents in France cost retailers tens of millions of euros, Thierry Cotillard, president of grocery giant Les Mousquetaires, told local media BFM TV.
Although two pro-Russian hacker groups claimed responsibility for the attacks, the Kremlin has denied Russia is responsible.
France on Nov. 9 blamed Iran’s Islamic Revolutionary Guard Corps for the hacks that hit hundreds of supermarkets across the country, calling it an “unprecedented campaign in terms of its scale and level of aggressiveness.”
The cyberattacks are believed to have been triggered by hackers who used the fridge systems’ internet connections to access them and then turn up the temperature dials.
After last month’s attack, France’s national cybersecurity agency urged stores to use a secure VPN connection to connect to the internet, install firmware updates, and change passwords.
Similar incidents across Europe have raised questions about whether supermarkets in the United States could soon become targets.
On Nov. 5, the U.S. Cybersecurity and Infrastructure Security Agency, the FBI, and the departments of Agriculture, Transportation, and Health and Human Services urged businesses in the United States to secure vulnerable controls of refrigeration systems used to store food and medicine.
Andy Jenkinson, fellow at the Cyber Theory Institute and author of the book “Stuxnet to Sunburst: 20 Years of Digital Exploitation and Cyber Warfare,” told The Epoch Times that the lack of a digital “air gap” was the short-term issue with the fridges.
The absence of an internet connection—known in the military and computer world as air gapping—makes systems much harder to hack.

A sign on an empty freezer reads “Due to cyberattacks, there will be no products available in the refrigerators/freezers. Our sincere apologies,” following an IT incident in Boortmeerbeek, Belgium, on Nov. 2, 2026. Maude Brulard/AFP via Getty Images
“Air gapping would stop attacks using internet connections to gain unlawful access,” Jenkinson said.
But he said while initial reports on the fridge attacks focus on legacy controllers and firmware, he believes the real threat is far more systemic.
Were US Military Commissaries Targeted?
“The recent cyberattacks targeting Danfoss and Sabcobel refrigeration systems across Europe are no longer just a commercial nuisance,” Jenkinson said. “The Pentagon is now actively investigating whether these same sophisticated tactics are linked to recent freezer malfunctions at multiple U.S. military commissaries.”
The Epoch Times reached out to Danfoss and Sabcobel for comment but did not receive a response by publication time.
[The fridge attacks] are a deliberate attempt to disrupt our food supply chain and undermine consumers’ confidence in it, a warning that we must take seriously.
Christophe Hansen, EU commissioner for agriculture and food
Stars and Stripes, Reuters, and Britain’s Daily Telegraph have all reported that U.S. military commissaries, including four in Germany and England and one at Fort Huachuca, Arizona, were suspected of being hit by cyberattacks earlier this year.
The U.S. Department of War (DOW) responded by email to The Epoch Times.
“We are aware of speculation regarding a potential cyber incident,” said a War Department spokesperson. “The Defense Criminal Investigative Service (DCIS), the criminal investigative arm of the DOW Office of Inspector General, is leading a joint investigation. For security reasons, we do not comment on ongoing law enforcement investigations.”

A woman walks past empty refrigerators at an Intermarché supermarket following a cyberattack in Névez, France, on Oct. 12, 2026. The attack caused the chain’s refrigerators to defrost. Fred Tanneau/AFP via Getty Images
The European Commission said the fridge attacks showed the disruptive potential of digital threats.
“They are a deliberate attempt to disrupt our food supply chain and undermine consumers’ confidence in it, a warning that we must take seriously,” EU commissioner for agriculture Christophe Hansen said. “The repeated occurrence of these cyberattacks is deeply concerning.”
The head of Britain’s National Cyber Security Centre (NCSC), Richard Horne, said at the NCSC Annual Review 2026 on Nov. 3 that if leaders of retail companies and other organizations do not deal with the situation quickly, they might soon have to explain themselves to their shareholders, customers, and employees when a bigger disaster hits.
“When food isn’t on the shelves, when lights aren’t on, businesses have gone under, we may have to explain that we saw the warning signs, understood the risks and still didn’t make the right choices,” he said.
Who’s Behind the Attacks?
So far, two pro-Russian hacker groups, NoName057(16) and Z-Pentest, claimed responsibility for the attacks in a post on Telegram.
But Oleg Shakirov, a Washington-based cyber policy and international security researcher, wrote in his Substack that there were significant reasons to doubt they were actually involved.
“Like other hacktivist actors, both NoName057(16) and Z-Pentest tend to exaggerate the impact of their activities,” Shakirov said. “So taking credit for one of the most discussed campaigns definitely won’t hurt.”

Employees throw spoiled food away outside a supermarket after a hacker attack raised the temperature in store freezers in Sjoebo, Sweden, on Nov. 2, 2026. Johan Nilsson/TT News Agency/AFP via Getty Images
Shakirov told The Epoch Times that NoName057(16) and Z-Pentest were more known for one-off opportunistic cyberattacks, rather than widespread campaigns.
He noted that in December 2025, Victoria Dubranova, 33, was indicted in connection with a cyberattack on a meat processing company in Vernon, Calif., that led to more than 2,000 pounds of meat being spoiled. She was extradited and charged with the attack, which was allegedly carried out by Z-Pentest, a group that is sometimes known as CyberArmyofRussia_Reborn (CARR).
Shakirov also said that in February 2022—just two days after Russia invaded Ukraine—Russian media reported that hacking collective Anonymous had compromised equipment at the Selyatino agricultural hub near Moscow and tried to spoil 40,000 tons of frozen food.
He said cyberattacks were sometimes financially motivated and sometimes politically motivated.
“But it just reminds us all of the fragility of this digital infrastructure,” Shakirov said.
On July 13, the FBI, the National Security Agency (NSA) and two other U.S. agencies joined Britain, France, Canada and nine other countries in sending out a cybersecurity advisory, warning of the threat posed to critical infrastructure networks by Russian cyber actors linked to Center 16, a wing of the Russian Federal Security Service allegedly funding a series of cyber bad actors.

A sign for the National Security Agency, U.S. Cyber Command, and Central Security Service near the entrance to the headquarters of the National Security Agency, in Fort Meade, Md., on Feb. 14, 2018. Saul Loeb/AFP via Getty Images
On Nov. 5, the Kremlin denied it was involved in the recent fridge attacks.
“These are absurd claims,” Kremlin spokesperson Dmitry Peskov told reporters. “As always, they are backed up by absolutely no reasoning, no evidence whatsoever, and yet here we have such baseless accusations against our country, implicating it in everything.”
Could the US Be Next?
Jason Radney, CEO of Coast2Coast MSP, an IT services company in Tampa Bay, Florida, said in an email to The Epoch Times that it was quite possible that the fridge attacks could occur in the United States.
“The same refrigeration and building-control equipment, and the same vendor remote-access habits, are common in American stores,” Radney said.
“I wouldn’t assume an ocean is any protection. Attackers tend to reuse what works, so U.S. chains should treat Europe as an early warning, not someone else’s problem.”
Tracy Guarino, a tech governance leader based in Nashville and CEO of Guarino Advisors, told The Epoch Times she had advice for every U.S. supermarket and grocery store wondering if the hackers would target America.
Attackers tend to reuse what works, so U.S. chains should treat Europe as an early warning, not someone else’s problem.
Jason Radney, CEO, Coast2Coast MSP
“What I’d say to every U.S. grocer is: don’t wait to find out,” Guarino said. “Find every controller in your supply chain, check whether it can be reached from the internet, and find out who holds the passwords.”
Guarino said examples in the Netherlands illustrate the importance of taking preventive action immediately.
“In the Netherlands, most shops had secured their systems after the French attack. The few that hadn’t were the ones hit,” Guarino said. “That’s the lesson: The preparation is much less expensive than a warm freezer.”

Shelves at an Albert Heijn supermarket are partially empty after a cyberattack at its parent company in Rotterdan, The Netherlands, on Oct.13, 2028. Robin Utrecht/ANP/AFP via Getty Images
Joel Goldstein, president of Mr. Checkout Distributors, a U.S. grocery supply chain, told The Epoch Times in an email that many smaller U.S. shops rely on direct store delivery routes and regional distributors who restock stores several times a week. A short refrigerator outage can get backfilled quite fast, he said.
“The big chains still run centralized building controls much like the European ones, so I wouldn’t assume they’re off the list,” Goldstein said.
What Should Supermarkets Do?
“Grocers should inventory every connected device, segment refrigeration and building systems from the business network, lock vendor remote access behind [multi-factor authentication] and time-limited approval, change default credentials, and keep manual temperature alarms that work when the network doesn’t,” Radney said.
Guarino said there were three crucial steps.
“First, vendor due diligence before any contract is signed, including how liability is allocated if the system fails,” Guarino said. “Second, a named owner for that risk, whether a board committee or an executive, because without one the risk sits with nobody.
The threat from state actors—Russia, North Korea, Iran—has grown immeasurably in the last nine years, and their capability with IT has also grown.
James Woudhuysen, professor, London South Bank University
“Third, defense-grade discipline for any system that can’t be allowed to fail.”
There is a cognitive gap between software engineers and those who maintain physical infrastructure, said James Woudhuysen, visiting professor of forecasting and innovation at London South Bank University.
“What do electronics and software engineers know about commercial fridges?” he told The Epoch Times.

People shop for groceries in New York on June 23, 2026. Samira Bouaou/The Epoch Times
“The threat from state actors—Russia, North Korea, Iran—has grown immeasurably in the last nine years, and their capability with IT has also grown,” Woudhuysen said.
He also criticized the assumption that virtual solutions can fix the “physical world” as “very foolish and very Silicon Valley.”
And while the vulnerability of supermarket fridges may be a relatively easy fix with air gapping, there are much bigger problems ahead, as was illustrated recently by the Binance crypto heist.
“As we witness the physical consequences of digital perimeter breaches, the rule is clear: access precedes exploitation,” Jenkinson said. “Until the foundational third-party dependencies are secured, this cyber-physical threat will only escalate.”
Unprecedented Cyber Risks Emerge Globally
On Oct. 29, hackers from North Korea stole $6.3 billion in cryptocurrency from Binance, the world’s biggest crypto exchange, in just four minutes.
The crypto assets themselves were not connected to the internet like supermarket fridges, but Binance said on Nov. 3 that expert hackers linked to North Korea used a range of techniques, including fake job interviews and malicious software downloads, to compromise the exchange’s internal artificial intelligence tooling and steal the $6.3 billion.
Vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale and pace that was once unimaginable.
Richard Horne, CEO, Britain’s National Cyber Security Centre
On Oct. 31, the FBI
said
it had identified a North Korean actor known as “TraderTraitor” as responsible for the Binance hack. On Nov. 3, Kim Yo Jong, the sister of North Korean leader Kim Jong Un,
denied
the FBI’s claims and called it “absurd rhetoric.”
Horne said the fridge incidents were “just the foothills” of a much greater problem which is looming for retailers, other companies, and institutions.

A Binance logo is displayed on a phone screen adjacent to an image of crypto exchange on a laptop in London on Oct. 30, 2026. Cybercriminals stole billions from the exchange in minutes. Dan Kitwood/Getty Images
“In the coming months, we face a real prospect of an unprecedented rise in the number of cyber incidents,” Horne said in a speech on Nov. 3. “But we must be clear, that is not because AI has invented new ways to attack us.”
“It is because vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale and pace that was once unimaginable,” Horne said in his speech.
“By 2028, it is highly likely China, Russia, and other nation states will routinely use AI cyber to achieve their geopolitical goals with the UK facing an increase in scale and speed of sophisticated cyberattacks,” the NCSC’s annual report said. The report also said AI-powered malware was a growing threat.
The Epoch Times reached out to Walmart, Costco, and Kroger for comment but did not receive a response by publication time.
Is Autumn Glow the Next Winx? Inside the Making of a Racing Superstar
Autumn Glow now has six Group 1 victories—and she is fast becoming...
Womens’ Rights Advocate to Run for One Nation in NSW
Former Liberal candidate for Warringah Katherine Deves waits for Prime Minister Scott...
MP Marks ‘Positive Moment’ in Recovery Following Car Ramming Attack Outside Office
Australian independent Member of Parliament Helen Haines speaks to journalists in the...
How a Secret Chinese Police ‘Liaison’ Officer in Vancouver Contacted a Student to Conduct ‘Ideological Work’
When a Chinese student in Vancouver stopped speaking to his parents, an...